
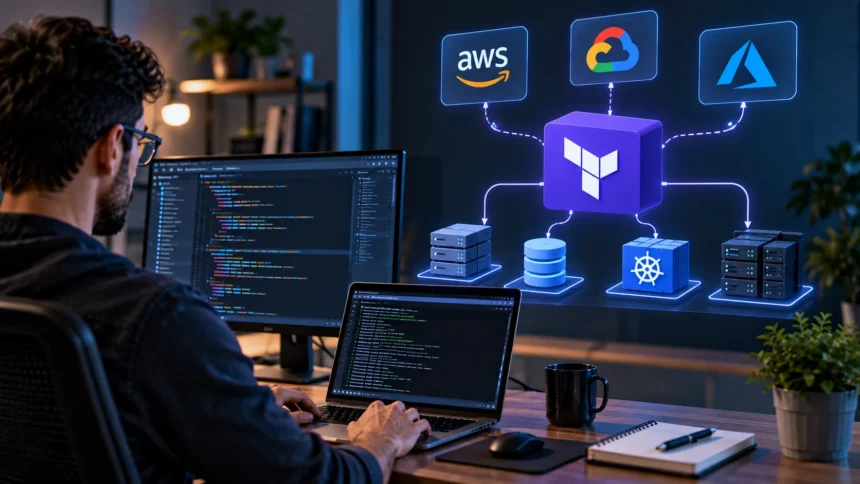
Terraform has become one of the most widely used tools for managing cloud infrastructure through code. Instead of manually creating servers, networks, databases, and other resources through cloud dashboards, DevOps teams can describe the infrastructure they want in configuration files. Terraform then helps create and manage those resources in a repeatable way.
This approach can make infrastructure easier to automate, review, reproduce, and scale across different environments. Terraform is especially useful for teams working with cloud platforms, DevOps pipelines, and modern application infrastructure. Understanding how Terraform works can help explain why Infrastructure as Code has become such an important part of software delivery.
What Is Terraform?
Terraform is an Infrastructure as Code tool developed by HashiCorp that allows teams to define and manage infrastructure through configuration files. Engineers describe resources such as virtual machines, databases, networks, storage, and load balancers using Terraform’s configuration language. Terraform then communicates with supported infrastructure providers to create or modify those resources.
Instead of administrators manually configuring every resource, Terraform turns infrastructure into something that can be documented and repeated. Configuration files can be stored in version control, reviewed by teammates, and updated over time. This creates a clear record of how infrastructure is supposed to look and how it changes.
Terraform is commonly used with public cloud platforms, private infrastructure, software-as-a-service platforms, and other technology providers. Its provider-based architecture allows teams to manage many different types of resources from one workflow. This flexibility is one of the main reasons Terraform has become popular with DevOps and cloud engineering teams.
How Does Terraform Work?
Terraform begins with configuration files describing the desired infrastructure. An engineer might define a virtual network, several servers, a database, and storage resources within those files. Terraform reads the configuration, compares it with the infrastructure that already exists, and determines what changes are required to reach the desired state.
Before making changes, Terraform can generate a plan showing which resources will be created, changed, or removed. This gives teams an opportunity to review the expected result before infrastructure is modified. Reviewing the plan can help prevent accidental changes and gives engineers greater visibility into what Terraform intends to do.
After the plan is approved, Terraform applies the changes through APIs provided by cloud platforms and other supported services. It creates or updates resources according to the configuration. If the infrastructure changes later, teams can update the Terraform files and repeat the process rather than manually modifying individual resources through separate dashboards.
Terraform and Infrastructure as Code
Terraform is closely associated with Infrastructure as Code because it turns infrastructure definitions into reusable configuration. Instead of relying on undocumented manual setup, teams describe what should exist using code-like files. This makes cloud infrastructure easier to reproduce and manage consistently across different projects and environments.
If you are new to the concept, understanding Infrastructure as Code first can make Terraform much easier to understand. IaC focuses on managing infrastructure through configuration rather than manual administration, while Terraform provides one practical way to implement that approach across supported platforms.
Using Terraform also allows infrastructure changes to follow software development practices. Teams can store configurations in Git repositories, create branches, review pull requests, and maintain a change history. Infrastructure therefore becomes something that can be tested, reviewed, and improved systematically rather than managed through isolated administrative actions.
Why DevOps Teams Use Terraform
DevOps teams value automation because manual infrastructure work can slow software delivery and introduce inconsistencies. Terraform lets engineers create repeatable environments without configuring every server, network, or database individually. This makes it easier to support development teams that frequently need new testing, staging, or production infrastructure.
Consistency is another important reason teams use Terraform. When the same configuration creates multiple environments, there is less chance that one system contains hidden settings missing from another. This can reduce configuration drift and make applications behave more predictably when they move from development into production.
Terraform also supports collaboration between development and operations teams. Infrastructure definitions can be discussed and reviewed just like application code. Developers gain more visibility into the infrastructure their applications require, while operations teams can create reusable standards that make deployment safer and easier to manage.
Terraform Providers Explained
Terraform providers are plugins that allow Terraform to communicate with different infrastructure platforms and services. A provider understands how to create, update, and delete specific resources through that platform’s API. Teams configure the provider and then define the infrastructure resources they want Terraform to manage.
Cloud providers are common examples, but Terraform’s provider ecosystem extends beyond basic cloud infrastructure. Teams may manage networking services, monitoring platforms, development tools, identity systems, databases, and other technologies depending on available provider support. This allows Terraform to coordinate different parts of an infrastructure environment through a consistent configuration approach.
Providers help make Terraform suitable for organizations using more than one technology platform. Instead of learning completely separate automation methods for every service, teams can manage supported resources through Terraform configurations. However, each provider still has its own resources, arguments, capabilities, and limitations that engineers must understand.
What Is Terraform State?
Terraform state is information Terraform maintains about the infrastructure resources it manages. It helps connect resources defined in configuration files with the real infrastructure created through cloud providers and other services. Terraform uses this information to understand what currently exists and determine what needs to change during future updates.
State becomes especially important when several resources depend on one another. Terraform can track resource identifiers, relationships, and selected attributes so later operations work correctly. Without accurate state information, the tool would have difficulty knowing whether it should create a new resource, modify an existing one, or leave infrastructure unchanged.
Teams must protect Terraform state carefully because it can contain sensitive infrastructure information. Shared environments also require a reliable method for storing and coordinating state between multiple engineers. Poor state management can lead to conflicts, unexpected changes, or difficulty understanding which infrastructure Terraform actually controls.
Terraform Modules and Reusable Infrastructure
Terraform modules allow teams to group related infrastructure configurations into reusable components. Instead of repeatedly defining the same network, server, database, or security configuration across projects, engineers can create a module once and reuse it with different input values. This can significantly reduce duplication in larger Terraform environments.
For example, a company might create a standard module for deploying web applications. The module could include networking, compute resources, security rules, and monitoring settings. Different teams could then use the same module while changing values such as application name, environment, instance size, or geographic region.
Reusable modules also help organizations create infrastructure standards. Security settings, naming rules, and architectural requirements can be built into approved configurations. Teams still need to review modules carefully because a mistake in a widely reused component can affect many environments when that module is updated or redeployed.
Terraform in CI/CD Pipelines
Terraform can be integrated into CI/CD pipelines so infrastructure changes follow automated review and deployment workflows. When someone modifies Terraform configuration, a pipeline can validate the files, check formatting, and generate a plan. Teams can review the proposed infrastructure changes before allowing them to reach production environments.
This approach reduces reliance on engineers running important infrastructure commands manually from individual computers. Automated pipelines can create a consistent process for validation and deployment. Access controls can also limit who can approve infrastructure changes, making production modifications easier to track and govern.
Infrastructure and application changes can sometimes move through coordinated pipelines. For example, an application release might require a new database or networking configuration before deployment. Terraform can prepare the required infrastructure while other CI/CD stages build, test, and release the application using a repeatable software delivery workflow.
Terraform Benefits for Cloud Infrastructure
One major benefit of Terraform is repeatability. Teams can create similar infrastructure across development, staging, and production without rebuilding everything manually. This reduces setup time and makes it easier to reproduce environments when projects expand, new teams are created, or systems need to be rebuilt after a failure.
Terraform can also improve visibility into infrastructure. Configuration files show what resources should exist and how they relate to one another. Engineers can review infrastructure design without navigating through many different cloud dashboards, which makes architecture easier to discuss, document, and troubleshoot.
Another benefit is scalability for operations teams. Managing a few cloud resources manually may be manageable, but hundreds or thousands of resources quickly become difficult to track. Terraform allows teams to automate repetitive provisioning and apply consistent patterns across larger environments without manually configuring each resource separately.
Common Terraform Challenges
Terraform has a learning curve, especially for engineers who are new to Infrastructure as Code. Teams need to understand configuration syntax, providers, resource dependencies, modules, state, variables, and infrastructure architecture. Learning the tool without understanding networking, cloud services, or security can also lead to poorly designed infrastructure.
State management creates another challenge. Multiple engineers working on the same environment need a coordinated process so they do not apply conflicting changes. State files must also be protected from unauthorized access and accidental modification because they play a critical role in Terraform’s understanding of infrastructure.
Terraform configurations can become difficult to maintain when projects grow without clear organization. Copying large blocks of code between environments may create unnecessary duplication, while overly complex modules can become difficult to understand. Teams need naming standards, documentation, modular designs, and regular code reviews to keep infrastructure manageable.
Terraform Best Practices
Store Terraform configuration in version control so every infrastructure change has a documented history. Use branches and peer reviews for important modifications, particularly changes affecting production. This allows teammates to examine resource deletions, security settings, networking changes, and unexpected cost implications before the configuration is applied.
Use reusable modules where they reduce duplication, but keep them focused and understandable. Avoid creating enormous modules that attempt to solve every infrastructure scenario at once. Smaller modules with clear purposes are easier to test, update, document, and reuse across different applications and environments.
Protect credentials and sensitive data carefully. Passwords, API keys, and secret values should not be hard-coded into Terraform files or committed to public repositories. Teams should also secure state files, restrict production permissions, review Terraform plans, and test significant infrastructure changes in lower-risk environments before applying them broadly.
Conclusion
Terraform is an Infrastructure as Code tool that allows DevOps teams to define and manage infrastructure through configuration files. It can automate resources such as networks, servers, databases, storage, and other services across supported platforms. This reduces dependence on repetitive manual infrastructure setup and creates more consistent environments.
DevOps teams use Terraform because it supports automation, repeatability, version control, collaboration, and scalable infrastructure management. Features such as providers, modules, state, and planning help engineers manage increasingly complex cloud environments. Terraform can also integrate with CI/CD workflows so infrastructure changes follow structured review and deployment processes.
Terraform is powerful, but successful adoption requires more than learning configuration syntax. Teams need solid cloud architecture, security, state management, review processes, and reusable infrastructure standards. When implemented carefully, Terraform can make infrastructure easier to reproduce, understand, scale, and maintain throughout the software delivery lifecycle.
FAQs
What is Terraform in simple terms?
Terraform is an Infrastructure as Code tool that lets teams describe cloud and technology resources in configuration files. It then uses those definitions to create, update, or remove infrastructure automatically.
Is Terraform a DevOps tool?
Yes. Terraform is widely used in DevOps for infrastructure automation, repeatable environment creation, version-controlled configuration, and integration with CI/CD workflows across cloud and other infrastructure platforms.
What is Terraform state used for?
Terraform state tracks information about infrastructure resources managed by Terraform. It helps the tool connect configuration definitions with real resources and determine what should change during future operations.
Can Terraform work with multiple cloud providers?
Yes. Terraform uses providers to communicate with supported platforms, allowing teams to manage resources across multiple cloud and technology services from Terraform configuration files.
Is Terraform difficult to learn?
Terraform basics are relatively approachable, but advanced usage requires understanding modules, state, providers, cloud architecture, networking, and security. Learning Infrastructure as Code concepts first can make Terraform easier to understand.